#Credential Theft
NIKKE PC Launcher Compromise Turns a Trusted Update Path into a Malware Delivery Channel
NIKKE PC Launcher Compromise Turns a Trusted Update Path into a Malware Delivery Channel The Windows PC launcher for Goddess of Victory: NIKKE was tampered with...

Lucas Oliveira
Research
MALFEX’s `imgdecode` Package Shows Why Native npm Addons Need Supply-Chain Scrutiny
MALFEX’s imgdecode Package Shows Why Native npm Addons Need Supply-Chain Scrutiny The latest MALFEX campaign has moved its most dangerous logic out of readable...
Lucas Oliveira
Research
ConnectWise SkyKick Credential Abuse Hits 173 Microsoft 365 Tenants
ConnectWise SkyKick: Compromised Credential Hits 173 M365 Tenants | 2026 Executive Summary Unknown threat actors used a compromised Microsoft 365 credential bel...
Lucas Oliveira
Research
Active Directory Compromise: 17 Techniques to Hunt
Active Directory Compromise: 17 Techniques to Hunt | 2026 Executive Summary CISA, NSA, ASD ACSC, the Canadian Centre for Cyber Security, NCSC-NZ and NCSC-UK upd...
Lucas Oliveira
Research
Malicious Browser Extensions Target Crypto Traders
Malicious Browser Extensions Target Crypto Traders | 2026 Executive Summary Socket Threat Research has disclosed a cross-browser extension operation targeting c...
Lucas Oliveira
Research
Cl0p Turns PTC Windchill Exploitation Into a Purpose-Built Extortion Platform
Cl0p Turns PTC Windchill Exploitation Into a Purpose-Built Extortion Platform Product lifecycle management systems are not usually the first asset class defende...
Lucas Oliveira
Research
Metabase zero-day turns BI dashboards into a data-exposure path
Metabase zero-day turns BI dashboards into a data-exposure path Metabase has confirmed active exploitation of CVE-2026-72898, a critical unauthenticated [SQL in...
Lucas Oliveira
Research
Swiss SharePoint breach shows why patching alone may not end the incident
Swiss SharePoint breach shows why patching alone may not end the incident Switzerland's federal IT office has confirmed a cyberattack against SharePoint servers...
Lucas Oliveira
Research
Windmill CVE-2026-29059 turns log access into a secrets problem
Windmill CVE-2026-29059 turns log access into a secrets problem Attackers are now exploiting CVE-2026-29059, a Windmill path traversal flaw that lets unauthenti...
Lucas Oliveira
Research
Vect and TeamPCP show how stolen build secrets become ransomware access
Vect and TeamPCP show how stolen build secrets become ransomware access Sophos says two cybercrime groups, Vect and TeamPCP, have formalized a partnership that...
Lucas Oliveira
Research
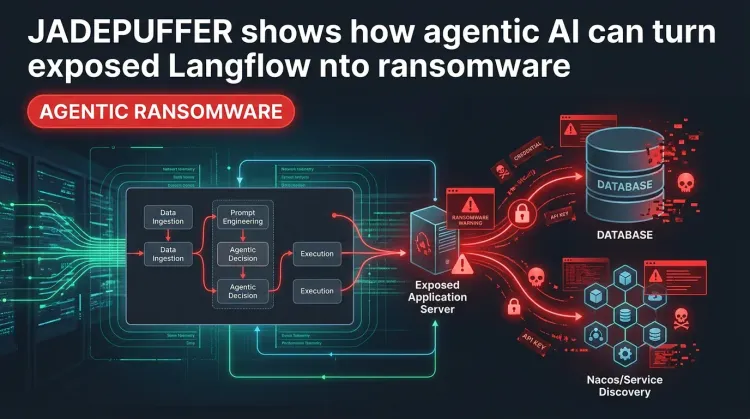
JADEPUFFER shows how agentic AI can turn exposed Langflow into ransomware
JADEPUFFER shows how agentic AI can turn exposed Langflow into ransomware Sysdig has documented what it assesses as one of the first clear examples of agentic r...
Lucas Oliveira
Research
SimpleHelp CVE-2026-48558 exploitation turns RMM into a credential-theft path
SimpleHelp CVE-2026-48558 exploitation turns RMM into a credential-theft path SimpleHelp has moved from patched vulnerability to active intrusion path. Attacker...
Lucas Oliveira
Research