#AI Security
PoeLLM Canto Incognito: The Botnet Hiding C2 in a GitHub Poem
PoeLLM Canto Incognito: The Botnet Hiding C2 in a GitHub Poem Executive Summary Lumen's Black Lotus Labs has tracked Canto Incognito, a financially motivated ca...

Lucas Oliveira
Research
SalesBleed shows how trusted AI agents can become data-exfiltration paths
SalesBleed shows how trusted AI agents can become data-exfiltration paths Salesforce Agentforce is the latest reminder that enterprise AI agents are not just ch...
Lucas Oliveira
Research
AI Agents Turned Retail Skimming Into a Low-Cost Cybercrime Pipeline
AI Agents Turned Retail Skimming Into a Low-Cost Cybercrime Pipeline A financially motivated operator has shown what happens when commodity offensive automation...
Lucas Oliveira
Research
AI Agents Turn Retail Skimming Into a Low-Cost Cybercrime Operation
AI Agents Turn Retail Skimming Into a Low-Cost Cybercrime Operation Executive Summary Gambit Security has documented an active campaign in which a financially m...
Lucas Oliveira
Research
CISA's New KEV Additions Put Edge and AI Control Planes on a Short Patch Clock
CISA's New KEV Additions Put Edge and AI Control Planes on a Short Patch Clock CISA's latest Known Exploited Vulnerabilities update is not just another list of...
Lucas Oliveira
Research
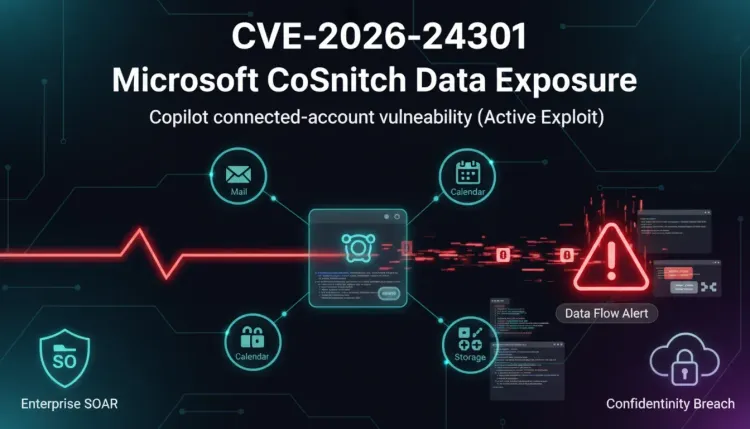
CVE-2026-24301: Microsoft Copilot CoSnitch Data Exposure
CVE-2026-24301: Microsoft Copilot CoSnitch Data Exposure CVE-2026-24301 is a newly published Microsoft Copilot vulnerability that turns a familiar enterprise ri...
Lucas Oliveira
Research
Hugging Face Diffusers flaws turn model loading into a code execution risk
Hugging Face Diffusers flaws turn model loading into a code execution risk Security researchers have disclosed a set of Hugging Face Diffusers vulnerabilities t...
Lucas Oliveira
Research
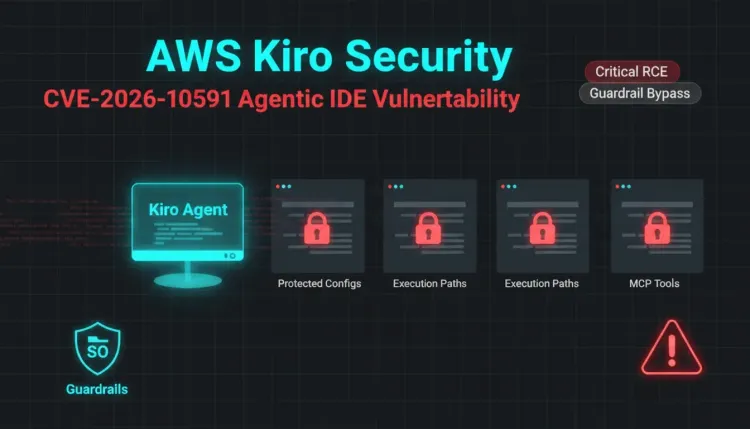
AWS Kiro flaw shows why AI coding agents need platform-level guardrails
AWS Kiro flaw shows why AI coding agents need platform-level guardrails AWS has patched a Kiro IDE security issue that captures one of the sharpest risks in age...
Lucas Oliveira
Research
AI-Assisted Linux Kernel Exploit Turns a Traffic-Control Race Into Root Access
AI-Assisted Linux Kernel Exploit Turns a Traffic-Control Race Into Root Access STAR Labs has published technical details for CVE-2026-53264, a Linux kernel race...
Lucas Oliveira
Research
ServiceNow CVE-2026-6875 turns AI workflow platforms into urgent patch targets
ServiceNow CVE-2026-6875 turns AI workflow platforms into urgent patch targets ServiceNow's July security advisory for CVE-2026-6875 has moved quickly from "cri...
Lucas Oliveira
Research
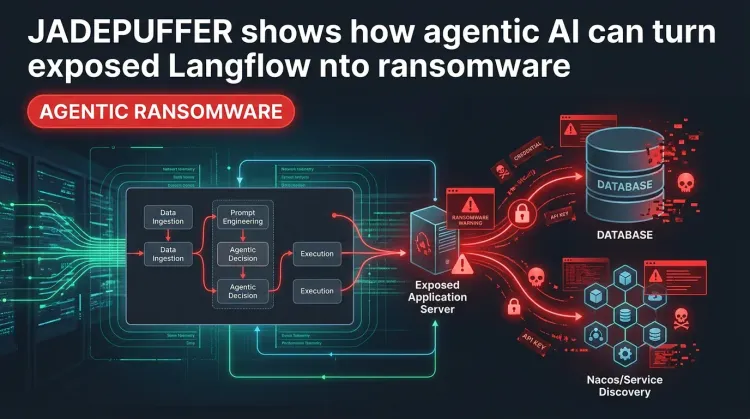
JADEPUFFER shows how agentic AI can turn exposed Langflow into ransomware
JADEPUFFER shows how agentic AI can turn exposed Langflow into ransomware Sysdig has documented what it assesses as one of the first clear examples of agentic r...
Lucas Oliveira
Research
Mastra npm compromise turns AI agent builds into credential-theft risk
Mastra npm compromise turns AI agent builds into credential-theft risk The Mastra npm incident is a sharp warning for teams building AI agents: dependency compr...
Lucas Oliveira
Research