#Threat Intel
ConnectWise Cloud Backup: Microsoft 365 Access Incident
ConnectWise Cloud Backup: Microsoft 365 Access Incident | 2026 Executive Summary On October 15, 2026, attackers abused a compromised ConnectWise Cloud Backup cr...

Lucas Oliveira
Research
PoeLLM Canto Incognito: The Botnet Hiding C2 in a GitHub Poem
PoeLLM Canto Incognito: The Botnet Hiding C2 in a GitHub Poem Executive Summary Lumen's Black Lotus Labs has tracked Canto Incognito, a financially motivated ca...
Lucas Oliveira
Research
ConnectWise SkyKick Credential Abuse Hits 173 Microsoft 365 Tenants
ConnectWise SkyKick: Compromised Credential Hits 173 M365 Tenants | 2026 Executive Summary Unknown threat actors used a compromised Microsoft 365 credential bel...
Lucas Oliveira
Research
Operation RapidRust shows APT36 evolving beyond simple phishing lures
Operation RapidRust shows APT36 evolving beyond simple phishing lures APT36, also tracked as Transparent Tribe, has a new campaign worth more than a passing mal...
Lucas Oliveira
Research
Malicious Browser Extensions Target Crypto Traders
Malicious Browser Extensions Target Crypto Traders | 2026 Executive Summary Socket Threat Research has disclosed a cross-browser extension operation targeting c...
Lucas Oliveira
Research
Splunk Enterprise CVE-2026-20253 hits KEV as exploitation begins
Splunk Enterprise CVE-2026-20253 hits KEV as exploitation begins Splunk's June 18, 2026 advisory update changed CVE-2026-20253 from a patch-now issue into an ac...
Lucas Oliveira
Research
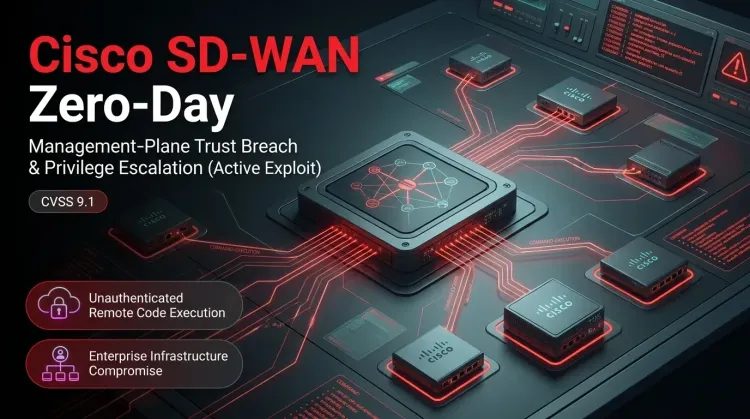
Cisco SD-WAN zero-day turns earlier auth bypass flaws into root access risk
Cisco SD-WAN zero-day turns earlier auth bypass flaws into root access risk Cisco's new CVE-2026-20245 advisory matters because it is not just another isolated...
Lucas Oliveira
Research
Palo Alto GlobalProtect auth bypass turns cookie trust into VPN access risk
Palo Alto GlobalProtect auth bypass turns cookie trust into VPN access risk CVE-2026-0257 matters because it turns a trust shortcut on the VPN edge into an iden...
Lucas Oliveira
Research
FortiClient EMS exploit turns endpoint management into credential theft at scale
FortiClient EMS exploit turns endpoint management into credential theft at scale CVE-2026-35616 matters because it breaks a security assumption many teams quiet...
Lucas Oliveira
Research
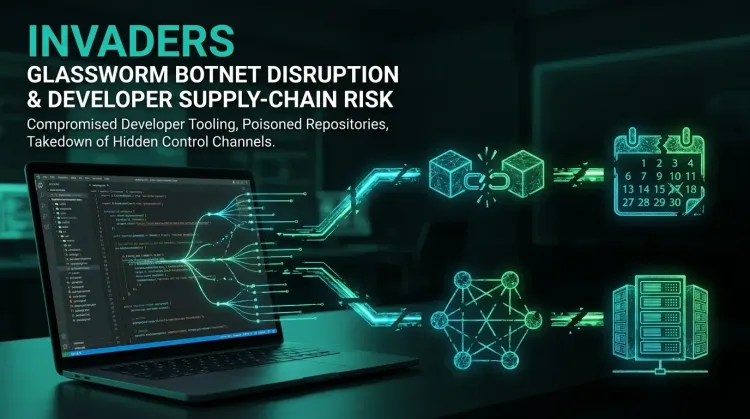
GlassWorm takedown shows how developer malware becomes supply-chain risk
GlassWorm takedown shows how developer malware becomes supply-chain risk Executive Summary The coordinated disruption of GlassWorm on May 26, 2026 is useful bec...
Lucas Oliveira
Research
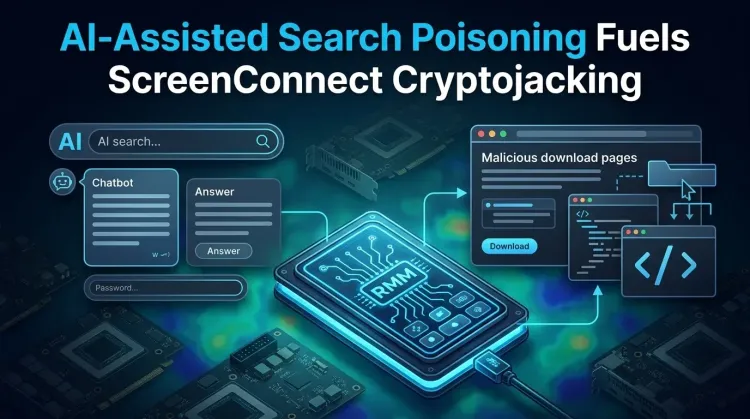
AI-Assisted Search Poisoning Fuels ScreenConnect Cryptojacking
AI-Assisted Search Poisoning Fuels ScreenConnect Cryptojacking Executive Summary Microsoft disclosed an active campaign on May 26, 2026 in which attackers push...
Lucas Oliveira
Research
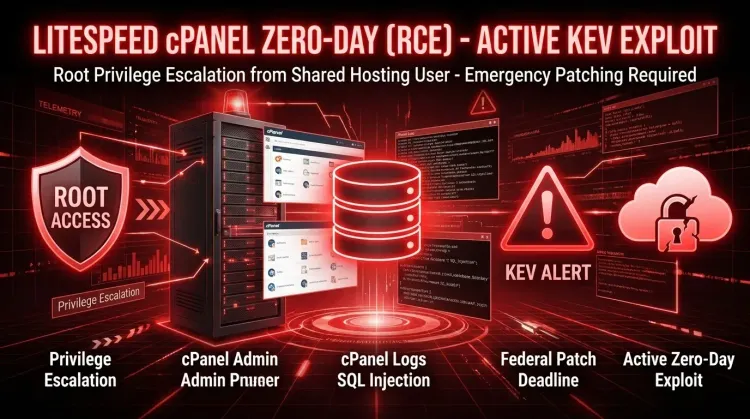
CVE-2026-48172 puts LiteSpeed cPanel deployments on a KEV deadline
CVE-2026-48172 puts LiteSpeed cPanel deployments on a KEV deadline CVE-2026-48172 has escalated from vendor emergency to federal patching priority. On May 26, 2...
Lucas Oliveira
Research