#Supply Chain Attack
Qubole AWS Trust Abuse Shows Why Dormant Cloud Integrations Stay Dangerous
Qubole AWS Trust Abuse Shows Why Dormant Cloud Integrations Stay Dangerous An attacker used credentials associated with Qubole's AWS account to enter multiple c...

Lucas Oliveira
Research
NIKKE PC Launcher Compromise Turns a Trusted Update Path into a Malware Delivery Channel
NIKKE PC Launcher Compromise Turns a Trusted Update Path into a Malware Delivery Channel The Windows PC launcher for Goddess of Victory: NIKKE was tampered with...
Lucas Oliveira
Research
XCPE Backdoor Turns Android TV Boxes into a Supply-Chain Botnet
XCPE Backdoor Turns Android TV Boxes into a Supply-Chain Botnet Google and industry partners have disrupted a backdoor that enrolled more than 1.3 million Andro...
Lucas Oliveira
Research
NetamLoader Targets Government Windows: The Update Folder Is Now a Hunting Surface
NetamLoader Targets Government Windows: The Update Folder Is Now a Hunting Surface Kaspersky’s discovery of NetamLoader shows how a highly tailored intrusion ca...
Lucas Oliveira
Research
Brevo breach turns trusted crypto newsletters into phishing channels
Brevo breach turns trusted crypto newsletters into phishing channels Executive Summary A compromise at Brevo, the email marketing provider used by several crypt...
Lucas Oliveira
Research
Mastra npm compromise turns AI agent builds into credential-theft risk
Mastra npm compromise turns AI agent builds into credential-theft risk The Mastra npm incident is a sharp warning for teams building AI agents: dependency compr...
Lucas Oliveira
Research
Red Hat npm compromise proves provenance alone is not enough
Red Hat npm compromise proves provenance alone is not enough Red Hat has confirmed that multiple packages published under the @redhat-cloud-services npm namespa...
Lucas Oliveira
Research
Cisco Breach Shows the Real Cost of the Trivy Supply-Chain Attack
Cisco Breach Shows the Real Cost of the Trivy Supply-Chain Attack The most important lesson from the Trivy incident is that a supply-chain attack on a trusted s...
Lucas Oliveira
Research
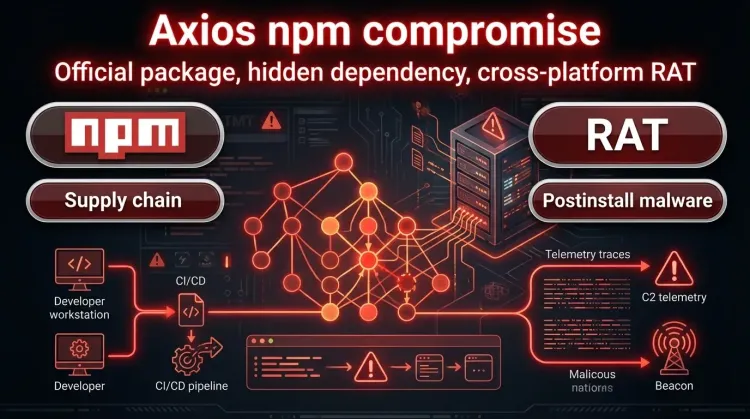
Axios npm compromise pushed a cross-platform RAT through a fake dependency
Axios npm compromise pushed a cross-platform RAT through a fake dependency A compromise of the widely used axios package on npm shows why defenders cannot rely...
Lucas Oliveira
Research