#Remote Code Execution
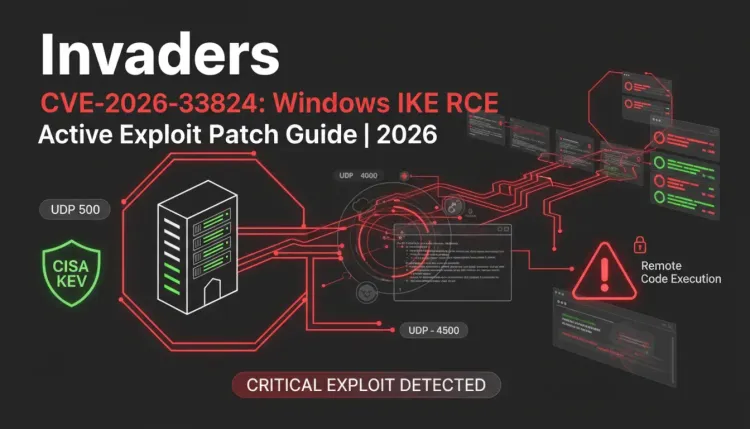
CVE-2026-33824: Windows IKE RCE Active Exploit Patch Guide
CVE-2026-33824: Windows IKE RCE Active Exploit Patch Guide | 2026 Executive Summary Since August 18, 2026, the critical CVE-2026-33824 vulnerability in Microsof...

Lucas Oliveira
Research
VMware vCenter RCE exploitation turns syslog exposure into persistence risk
VMware vCenter RCE exploitation turns syslog exposure into persistence risk VMware vCenter administrators should treat CVE-2026-59310 as more than a routine [vu...
Lucas Oliveira
Research
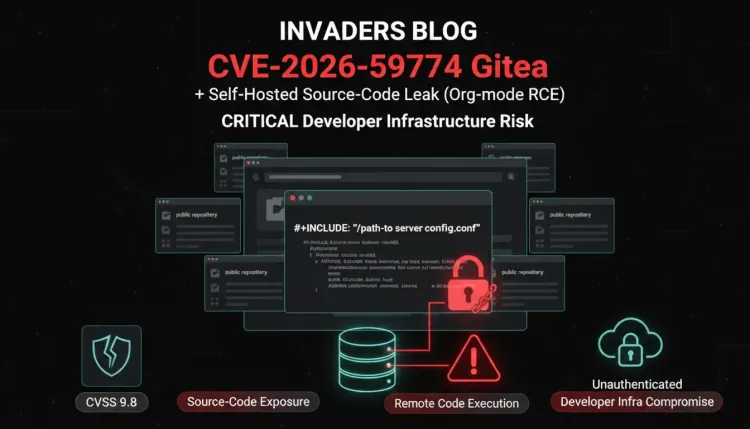
Gitea Org-mode flaw turns public repositories into a server file-read risk
Gitea Org-mode flaw turns public repositories into a server file-read risk Gitea administrators have a critical patch to verify. The project has fixed CVE-2026-...
Lucas Oliveira
Research
Hugging Face Diffusers flaws turn model loading into a code execution risk
Hugging Face Diffusers flaws turn model loading into a code execution risk Security researchers have disclosed a set of Hugging Face Diffusers vulnerabilities t...
Lucas Oliveira
Research
Adobe Campaign Classic flaws put on-prem marketing systems on the emergency patch list
Adobe Campaign Classic flaws put on-prem marketing systems on the emergency patch list Adobe has released an urgent security update for Adobe Campaign Classic a...
Lucas Oliveira
Research
AWS Kiro flaw shows why AI coding agents need platform-level guardrails
AWS Kiro flaw shows why AI coding agents need platform-level guardrails AWS has patched a Kiro IDE security issue that captures one of the sharpest risks in age...
Lucas Oliveira
Research
JetBrains TeamCity RCE Puts Self-Hosted CI/CD Servers on an Urgent Patch Clock
JetBrains TeamCity RCE Puts Self-Hosted CI/CD Servers on an Urgent Patch Clock JetBrains has released fixes for CVE-2026-63077, a critical unauthenticated [remo...
Lucas Oliveira
Research
Windmill CVE-2026-29059 turns log access into a secrets problem
Windmill CVE-2026-29059 turns log access into a secrets problem Attackers are now exploiting CVE-2026-29059, a Windmill path traversal flaw that lets unauthenti...
Lucas Oliveira
Research
SharePoint CVE-2026-50522 makes patching only the first step
SharePoint CVE-2026-50522 makes patching only the first step Microsoft SharePoint Server is back in the emergency lane. CVE-2026-50522, a critical deserializati...
Lucas Oliveira
Research
ServiceNow CVE-2026-6875 turns AI workflow platforms into urgent patch targets
ServiceNow CVE-2026-6875 turns AI workflow platforms into urgent patch targets ServiceNow's July security advisory for CVE-2026-6875 has moved quickly from "cri...
Lucas Oliveira
Research
7-Zip CVE-2026-14266 turns archive handling into an endpoint patch priority
7-Zip CVE-2026-14266 turns archive handling into an endpoint patch priority The latest 7-Zip security disclosure is not the kind of vulnerability that lets an a...
Lucas Oliveira
Research
NGINX CVE-2026-42533 turns a narrow map regex bug into an urgent patch window
NGINX CVE-2026-42533 turns a narrow map regex bug into an urgent patch window F5 has released fixes for CVE-2026-42533, a critical NGINX Plus and NGINX Open Sou...
Lucas Oliveira
Research