#CVE
Cisco patches another SD-WAN zero-day after limited exploitation
Cisco patches another SD-WAN zero-day after limited exploitation Cisco has disclosed yet another actively exploited weakness in its SD-WAN stack, and the import...

Lucas Oliveira
Research
YellowKey fix lands in June baseline: patch BitLocker fleets now
YellowKey fix lands in June baseline: patch BitLocker fleets now Microsoft has now closed the patch gap for CVE-2026-45585, the public BitLocker bypass widely r...
Lucas Oliveira
Research
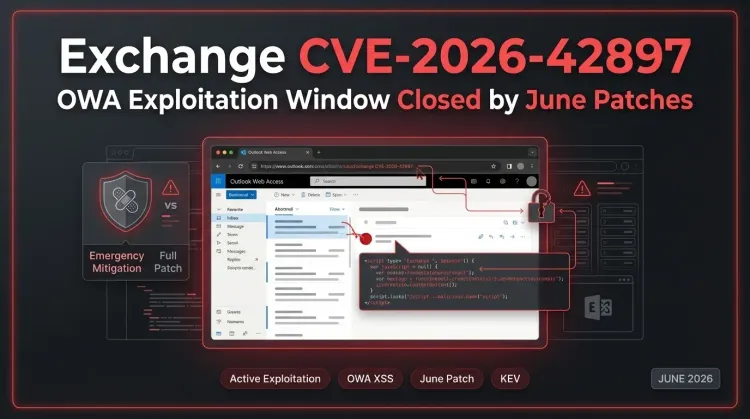
Exchange CVE-2026-42897 patches land after active OWA exploitation
Exchange CVE-2026-42897 patches land after active OWA exploitation Microsoft has now shipped the June 2026 Exchange security updates for CVE-2026-42897, ending...
Lucas Oliveira
Research
Veeam CVE-2026-44963 puts domain-joined backup servers at RCE risk
Veeam CVE-2026-44963 puts domain-joined backup servers at RCE risk Veeam has patched CVE-2026-44963, a critical [vulnerability](https://invaders.ie/resources/gl...
Lucas Oliveira
Research
Cisco CUCM SSRF bug turns WebDialer exposure into a path toward root
Cisco CUCM SSRF bug turns WebDialer exposure into a path toward root Cisco's latest Unified Communications Manager advisory deserves attention because it turns...
Lucas Oliveira
Research
CVE-2026-45247: Mirasvit Cache Warmer RCE Threatens Magento Stores
CVE-2026-45247: Mirasvit Cache Warmer RCE Threatens Magento Stores Executive Summary CVE-2026-45247 is a critical [vulnerability](https://invaders.ie/resources/...
Lucas Oliveira
Research
CVE-2026-48172 puts LiteSpeed cPanel deployments on a KEV deadline
CVE-2026-48172 puts LiteSpeed cPanel deployments on a KEV deadline CVE-2026-48172 has escalated from vendor emergency to federal patching priority. On May 26, 2...
Lucas Oliveira
Research
CVE-2026-45829: ChromaDB Pre-Auth RCE Risk in AI Stacks
CVE-2026-45829: ChromaDB Pre-Auth RCE Risk in AI Stacks | 2026 Executive Summary CVE-2026-45829 is a critical ChromaDB flaw that can let unauthenticated attacke...
Lucas Oliveira
Research
CVE-2026-42945 makes NGINX rewrite chains a live patch priority
CVE-2026-42945 makes NGINX rewrite chains a live patch priority CVE-2026-42945 has moved from fresh disclosure to active exploitation in days, which is exactly...
Lucas Oliveira
Research
CVE-2026-31431: Copy Fail turns routine Linux access into reliable root compromise
CVE-2026-31431: Copy Fail turns routine Linux access into reliable root compromise Copy Fail is the kind of Linux flaw defenders should not shrug off just becau...
Lucas Oliveira
Research
CVE-2026-41940 turns exposed cPanel and WHM servers into control-plane takeover targets
CVE-2026-41940 turns exposed cPanel and WHM servers into control-plane takeover targets CVE-2026-41940 is a critical authentication bypass in cPanel and WHM, an...
Lucas Oliveira
Research
CVE-2026-42208 turns exposed LiteLLM gateways into a secrets exposure risk
CVE-2026-42208 turns exposed LiteLLM gateways into a secrets exposure risk CVE-2026-42208 is a critical SQL injection flaw in LiteLLM's proxy API key verificati...
Lucas Oliveira
Research