Cybersecurity Research & Threat Intelligence
Research active vulnerabilities, cloud and application security, cybercrime, and supply chain risk with practical guidance for defenders.
Cybersecurity Research Coverage
Explore the research areas where Invaders publishes recurring analysis, from active exploitation and vulnerability management to cloud risk and supply chain security.
168 articles
Vulnerability Research
Active exploitation, CVEs, patch priorities, and exposure analysis.
52 articles
Threat Hunting & Intelligence
Threat actor activity, detection context, and defensive investigation guidance.
16 articles
Cloud & Application Security
Cloud platforms, web applications, identity, and engineering security risk.
20 articles
Cybercrime
Operational reporting on criminal ecosystems, breaches, and attacker activity.
5 articles
Supply Chain Security
Software delivery, third-party dependencies, and CI/CD trust boundaries.
Redis RESTORE Flaw Is Now Exploited: Patch CVE-2026-25243 and Restrict the Command
Redis RESTORE Flaw Is Now Exploited: Patch CVE-2026-25243 and Restrict the Command The Canadian Centre for Cyber Security has updated its Redis advisory to say...

Lucas Oliveira
Research
Capcom ID Breach Exposes 11.7 Million Records: The Phishing Risk Comes Next
Capcom ID Breach Exposes 11.7 Million Records: The Phishing Risk Comes Next Capcom has confirmed a [data breach](https://invaders.ie/resources/glossary/data-bre...
Lucas Oliveira
Research
Arista VeloCloud Orchestrator Zero-Day: Patch the SD-WAN Control Plane Now
Arista VeloCloud Orchestrator Zero-Day: Patch the SD-WAN Control Plane Now Arista has confirmed active exploitation of CVE-2026-114625, a critical [SQL injectio...
Lucas Oliveira
Research
CVE-2026-109618 and CVE-2026-109619: PHP2Shell RCE Exposure
CVE-2026-109618 and CVE-2026-109619: PHP2Shell RCE Exposure | 2026 Executive Summary CVE-2026-109618 and CVE-2026-109619 affect PHP runtimes and are collectivel...
Lucas Oliveira
Research
AOMEI Backupper Supply-Chain Attack: Hunt the Five-Minute Update Windows
AOMEI Backupper Supply-Chain Attack: Hunt the Five-Minute Update Windows Attackers compromised the update infrastructure used by AOMEI Backupper and briefly red...
Lucas Oliveira
Research
ConnectWise Cloud Backup: Why Disabling the App Is Only the First Step
ConnectWise Cloud Backup: Why Disabling the App Is Only the First Step ConnectWise is beginning a phased restoration of Cloud Backup, formerly SkyKick, after un...
Lucas Oliveira
Research
ConnectWise Cloud Backup: Microsoft 365 Access Incident
ConnectWise Cloud Backup: Microsoft 365 Access Incident | 2026 Executive Summary On October 15, 2026, attackers abused a compromised ConnectWise Cloud Backup cr...
Lucas Oliveira
Research
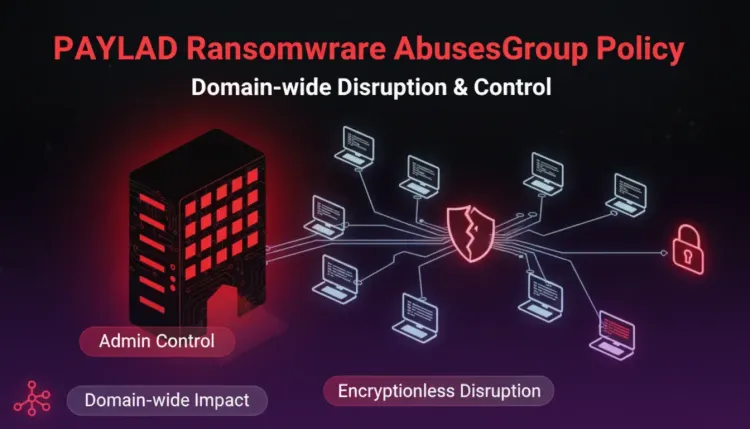
PAYLOAD Ransomware Turns Active Directory Group Policy Into a Domain-Wide Weapon
PAYLOAD Ransomware Turns Active Directory Group Policy Into a Domain-Wide Weapon Ransomware operators do not need to deploy an encryptor to create a business-wi...
Lucas Oliveira
Research
MALFEX’s `imgdecode` Package Shows Why Native npm Addons Need Supply-Chain Scrutiny
MALFEX’s imgdecode Package Shows Why Native npm Addons Need Supply-Chain Scrutiny The latest MALFEX campaign has moved its most dangerous logic out of readable...
Lucas Oliveira
Research
PoeLLM Canto Incognito: The Botnet Hiding C2 in a GitHub Poem
PoeLLM Canto Incognito: The Botnet Hiding C2 in a GitHub Poem Executive Summary Lumen's Black Lotus Labs has tracked Canto Incognito, a financially motivated ca...
Lucas Oliveira
Research
ConnectWise SkyKick Credential Abuse Hits 173 Microsoft 365 Tenants
ConnectWise SkyKick: Compromised Credential Hits 173 M365 Tenants | 2026 Executive Summary Unknown threat actors used a compromised Microsoft 365 credential bel...
Lucas Oliveira
Research
Microsoft Fixes Exploited Windows Shell Zero-Day Behind Mark-of-the-Web Bypass
Microsoft Fixes Exploited Windows Shell Zero-Day Behind Mark-of-the-Web Bypass Executive Summary Microsoft's October 2026 Patch Tuesday landed with an unusually...
Lucas Oliveira
Research